Cyber Economy Information Technology And Economy Seminar Report

Introduction to Cyber Economy Information Technology And Economy Seminar Topic:

Due to expanding IT industry it has a great influence on today’s global economy. In this paper we will discuss how IT industry is contributing for the development of Indian economy. The growth of software industry has as impact on the Indian economy and led to the growth of other organizational structures. The Indian companies are produce products related to both software and hardware and US is providing major share of projects for our IT industries.

Brief into cyber economy:

Unlike other countries which had abundant mineral sources, India has efficient skilled manpower. The Indian IT sector comprises of call centers, medical transcriptions, back office operations and revenue accounting and application building companies. Due to government policies for the development of software industries many companies from other countries started their companies with the collaboration of Indian companies and the companies are hiring Indians to work in their companies which are in abroad.

Due to this many people are getting work and we are able make software projects with effective cost and have high standards, for which many foreign companies are interested to give projects for our Indian companies. By this process a chain of business is going which increases the economic growth and helps in the development of the country. Due to this many people are showing interest to study professional courses and the literacy rate of the country is increasing.

Conclusion:

As the development of the IT industry has a impact on the economic growth, so every state should take certain measures to increase the growth of the industries. Due to the development of these industries they make our economy a globally developed economy and make our country an industrialized country. The development of the economy can improve the quality of various aspects and increases the income source of the country.

 Download  Cyber Economy Information Technology And Economy Seminar Report .
Seminar Report on Cyber Crime

Introduction to Seminar Topic  on Cyber Crime:

Cyber crimes are the increasing rapidly which has become a serious problem for the government. Cyber crimes are similar to that of conventional crimes, and here the computer is used for performing the crime. Cyber crimes are done by hackers who steal the data and misuse it or get hold of others network and perform financial crimes and email spoofing etc. in this paper we will elaborate how cyber crimes are performed and the preventive methods for reducing crimes.

Causes and types of cyber crimes:

Professional hackers perform cyber crimes by hacking websites or networks and they may steal information or crash the entire system which causes losses. Email bombing is a type of cyber crime where a large number of mails are sent to individual or a company which results in crashing of the data.

Salami attacks are performed in financial service providers like banks where the money from the accounts can be transferred to a particular account.  By Trojan attacks the access control of a computer or a network goes to the hacker and he can manipulate the data.  Many company like Microsoft and research organizations like NASA are facing many problems due to hackers.

Prevention methods and effects of cyber crimes:

Due to cyber crimes the provision of security to the services gets reduced. By virus attacks the networks may get crashed which causes loss of money. The companies have to appoint hackers so as increase the security levels. The security levels for the sites have to be increased so there will be a less chance for the hackers to hack. The government has to take severe action the persons committing cyber crimes so that other persons may not dare to violate the rules.

 Download  Seminar Report on Cyber Crime .

The Human Resources and TCO Total Cost of Ownership Literature Review

By making use of the different types of the storage resources in an efficient manner the storage consolidation is capable of offering the considerable savings of cost towards the traditional DAS. The major cost within the establishments of the DAS is that there is a necessity of managing the different systems in which the original storage is considered to be the primary cost within the NAS as well as SANs. The total number of the individuals who are needed to help the DAS entirely depends on the total numbers of the servers that are installed. Anyhow the servers are not being added by means of the SANs and the NAS they will just perform the storage process and for this reason there is only a necessity of the less number of users.

If the customers imagines the total numbers of the TB that belongs to the data could be easily controlled by means of the administrator run which is full time starts from 1.5 to 5.0 for the purpose of the DAS through the 6.0 to 13.3 for the purpose of NAS or SAN. On the other hand if the customer specifies that the usage of the disk is nearly 50% upon the DAS then that specific usage will increase nearly to the 90% which is intended for the purpose of the SAN as well as NAS. The SAN as well as NAs are capable of using the capacity that is available in an efficient manner and it is even simple to scale up the NAS and the SAN. 

Breakdown of the storage

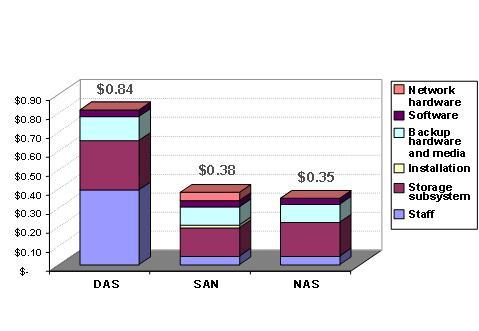
Fig: Breakdown of the storage costs per MB for the DAS, SAN as well as NAS. 

This figure will specify the procedure of cost breakdown for the purpose of the DAS, SAN and NAS. By this figure it is clear that the administration is the majority of cost for the DAS and the storage media is the majority of cost for the SAN as well as NAS.

The high availability, the reliability as well as the performance are the major reasons for the establishing the storage consolidation. The high availability is being used for the purpose of accessing the data without any interruption. The reliability is intended for the purpose of the decreasing the downtime and to improve the continuity of the business. The performance is meant for the purpose of processing the quick transaction in order to develop the entire productivity.

Each and every specified attributes could be easily accessed by making use of the SANs as well as NAS. There is a necessity of the several types of the equal systems in which one system will have no work to do that will even wait for the failure of the other system in order to perform this action. Within the entire process if the server of the DAS gets failed then the entire data storage which is associated with the server will not be available and the data can be restored when the server is restored. The process of decreasing the performance as well as the availability for allowing the data to be more vulnerable to the disturbances is the time consuming process and cannot be processed in an easy way. The final solution for the user to access without any interruptions is using the SAN or else the NAS which is not having any failures as well as using several numbers of the paths that are related to the data access times. The final conclusion is that it is better to use the SAN or NAS than that of the DAS.

Literature Review on Scaling Up And Out in NAS and SAN Technology

Because of the presence of more numbers of the smart switches the SANs as well as the NAS are capable of scaling up and out which could be surrounded by the unnecessary failure fabrics. By making use of the different types of the path these fabrics are capable of detecting the different failures as well as it will even redirect various requests of the users towards the mirror images.

By performing this process the availability of the user will not be disturbed and the servers as well as the storages will be added and then there is a necessity of the programmed downtime which is capable of decreasing the productivity of the user. The DAS is being connected with one or more number of the servers and if it uses the other server then it will not be able to access the capability of the server which is already used in the process.

The different types of the data of the users are being transferred by the SANs as well as NAs towards the available capacity. The storage which is unused can be allotted to the different servers by making use of the strategy called storage pooling. In order to attain the scalability of the performance the process of carrying out the storage consolidation is considered to be one of the best method.

File or Web and Database Applications in SAN and NAS Technology

The File or Web and Database Applications

The main concern within the process designing the storage consolidation is the access towards the different types of the applications. Each and every application will have its own methods and approaches for performing the process of data transfer. The major difference among the SAN and the NAS is the data transfer mechanisms through which the data is transferred by using some applications.

The SAN will move the huge chunks of data that is being transferred in a reliable manner by making use of the fabric protocol which depends on the different commands of the SCSI. But the NAS totally depends on the TCP or else the IP Ethernet which is capable of transmitting the small chunks of data. In different types of the circumstances the SANs are utilized as the subsystem of backend storage for the purpose of the installation of the large NAS in order to make the restore and backup tasks easy which will even decrease the traffic present within the networks of corporate.

The specific types of applications like the database and emails which utilizes the block access process in order to achieve the I/O on the data are considered to be the best applications that are more suitable to the SAN. The different applications could be easily balanced within each and every server towards any types of the storage fabrics.

By offering the on demand capability the storage is being distributed towards the different types of the servers. By decreasing the development and growth prices the reliable performance delivers the high bandwidth, the low latency interconnects as well as the switches of fibre channels. In the present circumstances related to the business there is always a necessity of the storing the consolidation applications in a success manner to improve the performance of the continuity systems of the business.

Latest CSE Seminar Topic on Backup and Restore in Network Storage Device

There is a necessity of the self tape backup or else the restore system to each and every DAS island which will have the group of tape cartridges along with the administrator for changing the cartridges of the tape. With the rapid increase within the growth of the islands the number of the cartridges will even increase along with the time period.

The SAN as well as the NAS are considered as the integrated storage that are capable of eradicating the different data copies and it will even be able to decrease the tasks and functions assigned to the administrator for carrying out the back up process. In order to improve or develop the performance of the tape devices they could be united with the different types of the tape backup farms.

By increasing the availability of the data the different types of the mirror copies of the data could be easily restored within the specified time from one part of SAN to NAS and NAS to SAN. This process will reduce the human based errors and it is even a cost effective process for the organizations.

CSE Seminar Topics 2012 on Network Buffer

Introduction to seminar topic on Network Buffer:

The multi server systems study in which many servers serve simultaneously the same queue, increased within the community of the computer with multiprocessors systems development in the 90s. With the mobile communications advance, more closely systems of multi server have become studied. For servers which are in multi server with restricted server number, specify K servers, the server development can be also classified as gate-limited and exhaustive-limited. In exhaustive-service, always all K servers are deployed as well as a service can be entered by a customer at a server which is empty while other services are serving other customers. This is named as Partial Batch Service.

For real systems many examples are presented which must be designed as systems of the gate-limited having bulk number of transport systems for example trains, buses etc. But with the internet emergence, distributed systems which are making use of semantics of client/ server can also be designed as bulk service of the gate-limited. Such system examples are network-based service in these systems, requests are being posted by the applications using the buffer of the network.

Then the buffer is transmitted over to server to these requests satisfaction. After the buffer arrived new systems has been transmitted, should in anticipation of replies to requests which are received previously have been revisited to the machine of the client, consequently this can be considered as system of the gate-limited multi server.

With Local Area Networks (LANs) faster development, services which are performed mostly on the machine which is local can be performed now over the network. One place in which many researchers are performed is in the storage area on other machines using the memory on a local area network to save information for example the Network Memory Server (NMS). This attempt has been concentrated on appearing at server way for example high-performance service can be offered by usage of the NMS such that the applications of the streaming can stream information without stalling while satisfying promptly misses of the demand to permit programs to sustain their execution. Such system can be displayed to be a system of a gate-limited however with requirements which are additional of identifying the perfecting amount as well as number of the misses of the demand which should be satisfied in a provided cycle.

To perform further investigation, a new model development was decided for gate-service depending upon Markov chains. Algorithms are developed using analytically model to balance demand paging as well as balance perfecting. Using a simulation testing was performed on this algorithm at the level of the system. Finally, to perform testing on this algorithm Experimental File System (EFS) was improved on a real system.

Queuing Systems Problems and Solutions

The queueing systems analysis has interesting but long history. In many practical systems this research result is implemented to serve customers from optimal strategies of queueing at centers of banking to systems which use token ring in computer networks which have high speed.

Some important results are yielded by these systems examination for example waiting time which is average for a customer in existed system or customer average in the system and to tackle normal performance issues for example under load how systems respond, etc. systems of queueing can be specified by using many parameters having the customer arrival time, the number of servers, and the service time. 

Traditionally service disciplines which have two types and variants of these things are observed. The first one is named as exhaustive service where everyone is served by the server in queue awaiting the empty queue.

This specifies that at the queue customers arriving while at the queue the server is existed are served during the present period of the service. Second one is named as gated service, where only the server serves the customers in the queue it finds at the service period beginning for that queue.

Basics of File Storage Process Literature Review

The file is considered as the set of the collection of the information which is rationally assembled into the group of single individual which is being referenced through the specific single name called filename. Basically there are two types of the end user devices such as data files such as the text documents, the spreadsheets, the images, videos and the system files like operating system, the binaries as well as the libraries of the applications.

The files are explained with their name as well as they are being stored managed and then accessed. The directories are so called the folders that can be considered as the organizational structures which are being utilized by the file systems towards the group files. The main purpose of the file systems is to secure and store the different types of the files, the system and data files, the metadata which is upon the storage media.

The lasting data is even maintained by the storage media which is considered as the data that is gathered from the deleted files. By making use of the end user devices as well as the forensic analysis process the lasting data could be recovered in an easy manner.

Threats of Different Types of Storage Devices Seminar Topic

In general in the recent time period there are different types of the existing threats related to the privacy of the information that is stored in the end user devices like the computers, the customer devices like phones, digital accessories, the different types of the removable storage devices such as the USB, memory card, the external hard drive, CD as well as DVD. The threats are of two types such as unintentional and the intentional.

The human based errors are referred to as the unintentional errors. The intentional threats will takes place because of the different types of motivations such as troubles and interruptions along with different attacks. The thefts and device losses are the major threats that will takes place in the end user devices. The other specific problem is that the individual who is having the physical access of the devices then that individual will be able to access and copy the information which is stored in those particular devices.

The other threat is that the insider attacks which means one employee accessing the information of the other employee by using the devices. The Malware is happened to be one of the other important threat which will allow the unauthorized access to the devices for the different attackers in order to transmit the information from the device that belongs to the attacker system and will carry out some activities such as the exposing the confidential information present in the device. The various types of threats that are towards the devices of end users will always allow access of the information present in it to the unauthorized users.

For protecting the information from these types of threats, there is a necessity of the using the strong security measures. There is even a need of protecting the components that belongs to the end user devices such as the operating system because it plays a vital role in storing the information. The encryption as well as the authentication is considered as the two significant aspects that can be used for the purpose of securing the data from the unauthorized access and users.

The encryption is the process which is applicable to the individual file which is having the secret information which will encrypt the entire data stored in the devices. The specific solutions for the encryption are totally based on the types of data, and quantity of data that is to be secured the environmental circumstances, location as well as the reduction levels of threats.

In general there are three different types of the encryption solutions for these threats such as the full disk encryption, the volume as well as the virtual disk encryption, the file or else the folder encryption. The specific encryption method is used based on the security requirements of the devices.